New website versionCurrent website

Vitaliy Pikov · Expert & lecturer

Secure development.
Engineering practice.

I help teams build secure software and teach the people behind it. Explore my lectures, practical workshops and resources for everyday engineering.

  • 26 years in IT
  • 10+ years of teaching
  • 40+ research publications
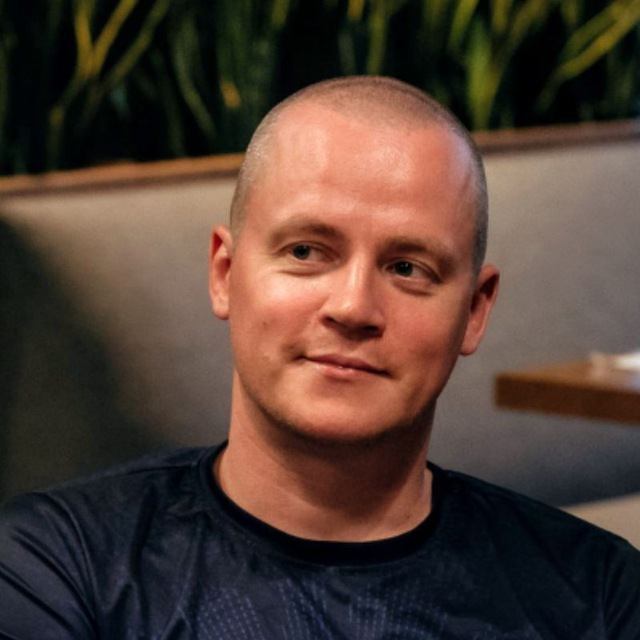
Vitaliy Pikov, secure software development expert and lecturer
Vitaliy PikovSecure development · AppSec · DevSecOps

Explore by subject

Different disciplines. One engineering perspective.

Materials

The material library

Lectures, courses, practical assignments and references, all in one place.

35 materials

The website is available in English and Russian. Lecture pages and teaching materials open in Russian.

Secure development

From requirements and architecture to code analysis and the software supply chain.

14 materials
LectureIn Russian

Requirements specifications: verifiable requirements and embedded secure development

How to write a specification that can actually be built and accepted: GOST 19 and 34 series, atomic requirements and acceptance test programmes.

Full description

How to write a specification that can actually be built and accepted: GOST 19 and 34 series, atomic requirements and acceptance test programmes. Secure development under GOST R 56939-2024 as the load-bearing axis — requirements → architecture → threat model → detection → remediation — with SAST/SCA/SBOM/fuzzing artefacts and an acceptance package.

Read the lecture
CourseIn Russian

Preparing for certification of secure development processes (FSTEC orders No. 240 and No. 230)

A complete methodology for preparing a security-product vendor for certification against GOST R 56939-2024: a road map, 25 process regulations and plans covering processes 5.1–5.25, a hardened C/C++ compiler…

Full description

A complete methodology for preparing a security-product vendor for certification against GOST R 56939-2024: a road map, 25 process regulations and plans covering processes 5.1–5.25, a hardened C/C++ compiler under GOST R 71206-2024, and verification via IDEF0 and AppSec Table Top.

Explore the course
LectureIn Russian

Languages, architecture and safe SQL

A teaching day on language classification and how technology choice affects security, on Shift Left, and on architectural trust boundaries.

Full description

A teaching day on language classification and how technology choice affects security, on Shift Left, and on architectural trust boundaries. Lab work: a hardened SQLite schema, CWE-89, parameterised queries, allowlists and the RED → GREEN cycle.

Read the lecture
CourseIn Russian

Application security: the two-day programme and its materials

A two-day educational lab: day 1 with a teaching slide deck, 15 original diagrams, a full transcript, a session protocol and lab materials; a glossary of 60+ terms and an instructor's guide; day 2 with the…

Full description

A two-day educational lab: day 1 with a teaching slide deck, 15 original diagrams, a full transcript, a session protocol and lab materials; a glossary of 60+ terms and an instructor's guide; day 2 with the programme and a prepared archive structure.

Explore the course
Practical workshopIn Russian

Application security: workshop and lab assignments

A method for local hands-on practice: isolating the Docker target, pinning the version, collecting evidence, classifying challenges, prevention for A01–A06, and report templates.

Full description

A method for local hands-on practice: isolating the Docker target, pinning the version, collecting evidence, classifying challenges, prevention for A01–A06, and report templates. Linked to the open archive of day-one source materials.

Open the workshop
LectureIn Russian

Information security and information security management systems

A five-lecture teaching day: security drivers and terminology, the ISO/IEC 27000 family, policy and RACI, the secure lifecycle under GOST R 56939-2024, risk management under ISO/IEC 27005, internal audit under…

Full description

A five-lecture teaching day: security drivers and terminology, the ISO/IEC 27000 family, policy and RACI, the secure lifecycle under GOST R 56939-2024, risk management under ISO/IEC 27005, internal audit under ISO 19011, and management review of the ISMS.

Read the lecture
ReferenceIn Russian

Threat catalogue for software security analysis

227 threats with affected objects and selection rationales: 177 apply to software directly or under stated conditions, while 50 fall outside the defined software analysis scope.

Full description

227 threats with affected objects and selection rationales: 177 apply to software directly or under stated conditions, while 50 fall outside the defined software analysis scope. Two coordinated lists with search, filters and CSV export. Content in Russian.
Open the reference

Systems & platforms

Astra Linux, Windows, hardware security and security tools.

8 materials
Practical workshopIn Russian

Hardening Astra Linux 1.7 / 1.8 and Linux systems

A systematic review of three documents from FSTEC of Russia (the federal technical and export control service): the 2022 Linux recommendations and the agreed guidance for Astra Linux 1.7 and 1.8.

Full description

A systematic review of three documents from FSTEC of Russia (the federal technical and export control service): the 2022 Linux recommendations and the agreed guidance for Astra Linux 1.7 and 1.8. Includes workstation and server checklists, 16 sysctl parameters, 6 “spot the flaw” cases and a 32-point readiness checklist.

Open the workshop
CourseIn Russian

KOMRAD Enterprise SIEM 4.5

An overview of this Russian SIEM by NPO Echelon, plus hands-on work on a VirtualBox lab: installation on Astra Linux 1.7/1.8, onboarding Windows 10 as an event source, the WMI agent, six national monitoring…

Full description

An overview of this Russian SIEM by NPO Echelon, plus hands-on work on a VirtualBox lab: installation on Astra Linux 1.7/1.8, onboarding Windows 10 as an event source, the WMI agent, six national monitoring standards and three practical exercises.

Explore the course

Regulation & law

Certification, licensing, risk management and critical infrastructure protection.

5 materials
LectureIn Russian

Day I. Security risk, protection of CII, incident response

A full teaching day from a professional retraining programme: information security risk management (GOST R ISO 31000-2019 and GOST R ISO/IEC 27005-2010); operation of protected systems and of significant…

Full description

A full teaching day from a professional retraining programme: information security risk management (GOST R ISO 31000-2019 and GOST R ISO/IEC 27005-2010); operation of protected systems and of significant critical information infrastructure (CII) facilities (Federal Law No. 187-FZ as amended in 2025, FSTEC orders No. 235, 239 and 117, and FSB regulations); planning of information-protection work; and computer incident management (GosSOPKA, the 597XX standards series). Five lectures of 1.5 academic hours, about 100 slides.

Read the lecture
LectureIn Russian

Day II. CII facilities: threats, controls, vulnerabilities

A deep dive into the security of critical information infrastructure: threat assessment (the FSTEC methodology of 5 February 2021 and the FSTEC threat database), the intruder model (N1–N4), the structure of a…

Full description

A deep dive into the security of critical information infrastructure: threat assessment (the FSTEC methodology of 5 February 2021 and the FSTEC threat database), the intruder model (N1–N4), the structure of a threat model with a worked case, control requirements under orders No. 235 and 239 (including trust levels for security products, database systems and virtualisation), how to select controls with a practical exercise, and vulnerability classification and criticality scoring under the FSTEC methodology of 30 June 2025. Five lectures of 1.5 academic hours, about 115 slides.

Read the lecture

Security testing

Pentesting, fuzzing and static analysis: methods and practice.

5 materials
CourseIn Russian

Attacker techniques and infrastructure security assessment

An original course on attack methodology and penetration testing: 5 lectures plus a hands-on session on Kali Linux and Metasploitable 2.

Full description

An original course on attack methodology and penetration testing: 5 lectures plus a hands-on session on Kali Linux and Metasploitable 2. FSTEC regulation, the FSTEC vulnerability database, Russian tooling, Articles 272–274.1 of the Russian Criminal Code, and the PTES methodology.

Explore the course
CourseIn Russian

Penetration testing, advanced (10 days)

An advanced course for practising pentesters, SOC analysts and DevSecOps engineers: 12 modules, OWASP Top 10, reverse engineering, EDR evasion, Active Directory post-exploitation and a final assessment project.

Full description

An advanced course for practising pentesters, SOC analysts and DevSecOps engineers: 12 modules, OWASP Top 10, reverse engineering, EDR evasion, Active Directory post-exploitation and a final assessment project. Has its own detailed landing page.

Explore the course
CourseIn Russian

Fuzz testing for secure software development

A dynamic-analysis course for security-product developers, certification-body experts and DevSecOps engineers: AFL++, libFuzzer, Sydr-Fuzz, and fuzzing of compiled, web and systems languages under GOST R…

Full description

A dynamic-analysis course for security-product developers, certification-body experts and DevSecOps engineers: AFL++, libFuzzer, Sydr-Fuzz, and fuzzing of compiled, web and systems languages under GOST R 56939-2024 (process No. 11).

Explore the course

Study & references

Information systems design, graduation projects and SPDX licences.

3 materials

Choose your starting point

A suggested order for building knowledge and putting it to work.

Getting started

Learn the language of security

Understand assets, threats and risk. Start by mapping the boundaries of a simple information system.

Start with information systems

Administrators & security engineers

Build a system you can verify

Work through configuration, hardening and monitoring. Check what changed and how to roll it back.

Start with Astra Linux

Developers & DevSecOps

Bring security into development

Connect architecture, threat modelling, code analysis and software composition with evidence of the result.

Start with secure development

Engineering, research and teaching.

My work brings together secure software development, information security and education. I translate requirements into architecture, working processes and checks that teams can use.

  • Secure C/C++
  • SCA & SBOM
  • AppSec & DevSecOps
  • Threat modelling
More about my background

Let’s work on the next step.

For lectures, team training and consulting on secure software development and information security.