Авторский каталог · информационная безопасностьOriginal course catalogue · information security
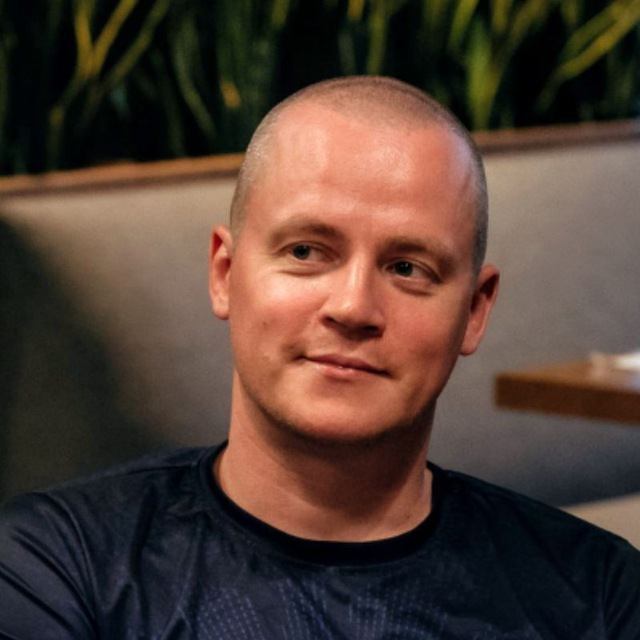
Пиков Виталий АлександровичVitaliy Pikov
Эксперт по безопасной разработке ПО, DevSecOps и AppSec; преподавательExpert in secure software development, DevSecOps and AppSec; lecturer
26 лет в ИТ, более 10 лет преподавательской работы. Заслуженный доцент РосНОУ. Авторизованный преподаватель «Группы Астра» с правом проведения курсов по ОС Astra Linux Special Edition 1.8.26 years in IT, more than 10 years of teaching. Honoured Associate Professor of RosNOU (Russian New University) — an honorary university title. Authorised instructor for Astra Group, certified to deliver courses on Astra Linux Special Edition 1.8.
Это не жёсткие программы, а рекомендуемая последовательность. Начните с ближайшей роли, зафиксируйте итоговый артефакт и переходите к следующему уровню только после проверки результата.These are not rigid syllabi but a recommended order. Start from the role closest to you, produce the final artefact, and move on to the next level only once the result has been checked.
Уверенная работа с компьютером; базовые понятия ОС и сети.Confident computer use; basic operating-system and networking concepts.
ДлительностьDuration
6–8 академических часов.6–8 academic hours.
РезультатOutcome
Объяснить актив, угрозу, уязвимость, риск, меру и границу информационной системы.Explain asset, threat, vulnerability, risk, control and the boundary of an information system.
АртефактArtefact
Одностраничная карта активов, границ и пяти основных рисков учебной системы.A one-page map of assets, boundaries and the five principal risks of a training system.
Администратор и специалист по ИБAdministrator and security engineer
Платформа, hardening и наблюдаемостьPlatform, hardening and observability
ПредпосылкиPrerequisites
TCP/IP, командная строка Windows/Linux, принципы учётных записей и журналирования.TCP/IP, the Windows/Linux command line, account management and logging fundamentals.
ДлительностьDuration
2–3 учебных дня с локальным стендом.2–3 teaching days with a local lab.
РезультатOutcome
Проверить конфигурацию, применить безопасное изменение, собрать доказательства и выполнить rollback.Audit a configuration, apply a safe change, collect evidence and roll the change back.
АртефактArtefact
Паспорт стенда, чек-лист hardening и отчёт «до → изменение → тест → откат».A lab specification, a hardening checklist and a “before → change → test → rollback” report.
Разработчик и DevSecOpsDeveloper and DevSecOps
Security-by-design и цепочка поставкиSecurity by design and the supply chain
ПредпосылкиPrerequisites
Git, один язык программирования, сборка и базовый CI/CD; для native-трека — C/C++.Git, one programming language, build tooling and basic CI/CD; C/C++ for the native track.
ДлительностьDuration
2–3 учебных дня плюс самостоятельная лабораторная работа.2–3 teaching days plus independent lab work.
РезультатOutcome
Провести threat modeling, проверить зависимости, найти дефект, исправить его и доказать исправление тестом.Run threat modeling, review dependencies, find a defect, fix it and prove the fix with a test.
АртефактArtefact
Модель угроз, SBOM/решение о допуске компонента и finding с negative test и retest.A threat model, an SBOM with a component-approval decision, and a finding with a negative test and a retest.
The courses themselves are taught and published in Russian. This catalogue page is available in English so you can see the scope of the work; every linked lecture, slide deck and handout opens in Russian. Write to vitaly@pikov.expert if you need an English-language session or materials.
/
По запросу ничего не найдено.Nothing matches your query.
Обо мнеAbout
Безопасная разработка, инженерная практика, преподавание и научная работа — от требований и архитектуры до проверяемых артефактов и работающих инструментов.Secure development, engineering practice, teaching and research — from requirements and architecture through to verifiable artefacts and working tools.
Я занимаюсь безопасной разработкой программного обеспечения, DevSecOps и AppSec: помогаю превращать требования стандартов в архитектурные решения, рабочие процессы, автоматизированные проверки и проверяемые результаты. В центре практики — security-by-design, моделирование угроз и защита на всём жизненном цикле ПО.I work in secure software development, DevSecOps and AppSec, turning the requirements of standards into architectural decisions, working processes, automated checks and verifiable results. At the centre of that practice are security by design, threat modeling, and protection across the whole software lifecycle.
Secure C/C++
SAST и DASTSAST & DAST
ФаззингFuzzing
SCA и SBOMSCA & SBOM
Software Supply Chain
DevSecOps
AppSec
Профессиональный путьProfessional background
Более 25 лет работаю на стыке информационных технологий, информационной безопасности, исследований и образования: участвовал в разработке защищённых вычислительных систем, формировании требований безопасности, экспертизе архитектуры и исходного кода, испытаниях средств защиты и управлении техническими командами.For more than 25 years I have worked at the intersection of information technology, information security, research and education: developing trusted computing systems, defining security requirements, reviewing architecture and source code, testing security products, and leading engineering teams.
Последнее место службы — профильный научно-исследовательский институт государственного сектора. Там прошёл путь от инженера-программиста до руководителя научно-исследовательской лаборатории по защите информации и испытательной лаборатории. После службы занимался защищёнными вычислительными платформами, развитием программ дополнительного образования и практическим внедрением процессов РБПО.My last position in public service was at a specialised state-sector research institute. There I progressed from software engineer to head of a research laboratory for information protection and of a testing laboratory. Since then I have worked on trusted computing platforms, on developing continuing-education programmes, and on the practical rollout of secure software development processes.
Инженерная практикаEngineering practice
Выстраиваю РБПО не только как комплект документов, но и как действующий инженерный контур. Создал и внедрил внутренний сервис SCA/SBOM для компонентного анализа, учёта уязвимостей и проверки лицензионной чистоты сторонних компонентов.I build a secure development lifecycle as a working engineering loop, not merely a set of documents. I designed and rolled out an in-house SCA/SBOM service for component analysis, vulnerability tracking and licence-compliance review of third-party components.
Работаю с CycloneDX, SPDX, VEX/OpenVEX и CSAF; обогащаю данные из NVD, OSV, EPSS и CISA KEV. Встраиваю ролевой доступ, неизменяемый аудит, контейнеризацию и security gates в CI/CD. Для C/C++ делаю акцент на безопасности памяти, безопасных API, compiler hardening, санитайзерах, SAST, DAST и фаззинге.I work with CycloneDX, SPDX, VEX/OpenVEX and CSAF, enriching data from NVD, OSV, EPSS and CISA KEV. I embed role-based access, immutable audit, containerisation and security gates into CI/CD. For C/C++ the emphasis is on memory safety, safe APIs, compiler hardening, sanitizers, SAST, DAST and fuzzing.
Стандарты и методологииStandards and methodologies
Соединяю российские нормативные требования с международными инженерными практиками: требования, архитектура, модель угроз, код, тестирование, состав компонентов и выпуск продукта образуют единую проверяемую цепочку.I connect Russian regulatory requirements with international engineering practice, so that requirements, architecture, threat model, code, testing, component inventory and release form one verifiable chain.
ГОСТ Р 56939-2024GOST R 56939-2024
ГОСТ Р 71207-2024GOST R 71207-2024
NIST SSDF
OWASP SAMM
OWASP ASVS
CWE
ISO/IEC 27001
ISO/IEC 27034
CERT C/C++
MISRA C/C++
ПреподаваниеTeaching
Более 10 лет преподаю в высшей школе и дополнительном профессиональном образовании.More than 10 years of teaching in higher education and in continuing professional education.
Подготовил к успешной защите более 130 студентов: бакалавров, специалистов и магистров, включая ВКР по информационной безопасности и информационным системам.Supervised more than 130 students to a successful defence at bachelor's, specialist (the five-year Russian first degree) and master's level, with final qualification theses on information security and information systems.
Разработал 10 авторских курсов по РБПО, статическому и динамическому анализу, фаззингу и тестированию на проникновение.Authored 10 original courses on secure software development, static and dynamic analysis, fuzzing and penetration testing.
Обучил более 100 специалистов и провёл более 40 вебинаров по безопасной разработке, включая большой совместный цикл с PVS-Studio.Trained more than 100 practitioners and delivered more than 40 webinars on secure development, including an extensive joint series with PVS-Studio.
Наука и публичная экспертизаResearch and expert engagement
Автор более 40 научных публикаций по информационной безопасности, безопасной разработке, аппаратным уязвимостям и защищённым информационным системам; работы представлены в Scopus и Web of Science.Author of more than 40 research publications on information security, secure development, hardware vulnerabilities and trusted information systems; indexed in Scopus and Web of Science.
Приглашённый эксперт круглого стола по безопасной разработке на МиТСОБИ 2026.Invited expert on the secure-development round table at MiTSOBI 2026.
Докладчик Positive Hack Days, Инфофорума, InfoSecurity Russia и международных научных конференций; эксперт соревнований по информационной безопасности.Speaker at Positive Hack Days, Infoforum, InfoSecurity Russia and international academic conferences; judge at information-security competitions.
Образование и квалификацияEducation and qualifications
Базовое инженерное образование дополнено системной профессиональной переподготовкой и регулярным повышением квалификации в области ИБ, безопасной разработки, педагогики и искусственного интеллекта.A foundation in engineering, extended by systematic professional retraining and regular continuing education in information security, secure development, pedagogy and artificial intelligence.
Базовое высшее образованиеPrimary degree
Высшее инженерное образование по специальности «Автоматизированные системы обработки информации и управления».Engineering degree in Automated Information Processing and Control Systems.
Педагогика профессионального образования и дополнительного профессионального образования.Pedagogy for vocational and continuing professional education.
«Техническая защита информации».Technical protection of information.
«Практическая психология».Applied psychology.
«Искусственный интеллект в образовании».Artificial intelligence in education.
Повышение квалификации и дополнительная подготовкаContinuing education and additional training
Безопасность приложений.Application security.
Современная ИБ: подходы, инструменты и образовательные практики.Contemporary information security: approaches, tooling and teaching practice.
«Специалист по процессам разработки безопасного программного обеспечения», 200 часов; анализ архитектуры и экспертиза исходного кода; Python, обработка радиолокационной информации, нейронные сети, этика ИИ и качество преподавания ИТ.Secure Software Development Process Specialist, 200 hours; architecture analysis and source-code review; Python, radar signal processing, neural networks, AI ethics and quality in IT teaching.
2022–2023KasperskyOS, информационная безопасность АСУ ТП и современные киберугрозы.KasperskyOS, industrial control system security and the current threat landscape.
Администрирование Astra Linux Special Edition.Astra Linux Special Edition administration.
2009–2010Системное администрирование, Windows Server, Active Directory и развёртывание Windows.Systems administration, Windows Server, Active Directory and Windows deployment.
Звания и профессиональные статусыTitles and professional standing
Заслуженный доцент РосНОУ, преподаватель высшей школы.Honoured Associate Professor of RosNOU — an honorary title conferred by the Russian New University, not an academic rank or degree. Higher-education lecturer.
Авторизованный преподаватель по Astra Linux Special Edition 1.7/1.8.Authorised instructor for Astra Linux Special Edition 1.7/1.8.
Microsoft Certified: MCT, MCITP, MCPS, MCSA, MCTS.Microsoft Certified: MCT, MCITP, MCPS, MCSA, MCTS — including Microsoft Certified Trainer (MCT).
СвязьContact
По вопросам лекций, курсов и консультаций в области информационной безопасности.For lectures, courses and consulting on information security.